Repository navigation
Conversation


E2E Test ReportEnvironment
Process output visibility
Auto-scroll and copy
Automated verification
Not manually covered
|
…utput

# Conflicts:
#	packages/cli/src/acp-integration/acpAgent.ts
#	packages/cli/src/serve/routes/session.ts
#	packages/cli/src/serve/server.test.ts
#	packages/cli/src/serve/server/telemetry-catalog.test.ts
#	packages/cli/src/serve/server/telemetry.test.ts
#	packages/sdk-typescript/test/unit/DaemonClient.test.ts
#	packages/web-shell/client/components/messages/TasksStatusMessage.test.tsx

 qqqys
left a comment
qqqys
left a comment
There was a problem hiding this comment.
Critical-only review at head b03ea9d.
Previously blocking issue — fixed. R1-10 reported that _qwen/session/tasks/output was dispatchable but absent from ALL_QWEN_VENDOR_METHODS, so initialize never advertised it and feature-detecting ACP clients would skip the method. Commit 5e8d3bd adds the entry (dispatch.ts:286) alongside the three sibling session/tasks* methods and pins it with a transport assertion.
No new Critical found. Checked the blocking-risk surfaces:
- Route scope.
GET /session/:id/tasks/:taskId/outputgoes throughwithOwnerReadSession; the WS case usesrequireOwned(read path, matching siblingsession/tasks) and is registered inWS_READ_METHODS. No primary-runtime or cross-session fallback. - File access. Output is resolved by
taskIdinside the owning session's ownbackgroundShellRegistry/monitorRegistry— no client-supplied path reaches the filesystem. The read reusesreadTaskOutputTailwith itsO_NOFOLLOW+fstatidentity guard, control/bidi sanitization, and the 64 KiB clamp; fs errors map to a genericTask output is unavailable.rather than leaking the path or errno. - Reader refactor. The new
maxBytesparameter defaults toMAX_NOTIFICATION_OUTPUT_TAIL_BYTES, and the length is clamped byMath.min(stat.size, maxBytes, MAX_TASK_OUTPUT_TAIL_BYTES), so the pre-existing notification caller keeps its 8 KiB behavior unchanged. - Monitor writer lifecycle. The write stream is created before spawn and torn down on every exit path — spawn failure (both catch blocks), abort handler, and normal cleanup — with an
errorlistener attached, so a failed or late write degrades to a warning instead of an unhandled crash. - UI.
ProcessTaskOutputcalls all hooks before itsif (!supported) return nullcapability gate, so hook order stays stable across daemons with and withoutsession_task_output; the remountkeyand effect deps prevent stale cross-task output.
Remaining review-round items are Suggestions (untested in-band error path, uncapped monitor output growth, read-permission roots for the advertised monitor path, first-mount scroll anchoring, terminal-task retry) and are not merge blockers.
CI at this head is still settling after the merge from main; no failure is attributable to this PR. The earlier red integration run came from the missing session_task_output capabilities baseline, which eaaa16d added.
|
@qwen-code /triage |
qqqys
left a comment
qqqys
left a comment
There was a problem hiding this comment.
Re-reviewed at head acd56a4d; my earlier approval was dismissed by this push, so this covers the new commit as well as the unchanged production diff.
Previously blocking issue — still fixed. The one Critical from the prior round (R1-10: _qwen/session/tasks/output was dispatchable but absent from ALL_QWEN_VENDOR_METHODS, so initialize never advertised it and feature-detecting ACP clients would skip the method) remains resolved on this head — the entry is present at dispatch.ts:286 alongside the three sibling session/tasks* methods, with the transport assertion from 5e8d3bd.
The new commit is docs-only and accurate. acd56a4d changes one line in docs/developers/daemon/00-index.md, moving the registered-capability count from 151 to 152 to account for the session_task_output tag this PR adds. Verified against the code: SERVE_CAPABILITY_REGISTRY on this head has exactly 152 top-level tag entries with no duplicates and includes session_task_output. No production file changed, so the diff reviewed below is byte-identical to the previously approved revision.
No Critical found in the production diff. Checked the blocking-risk surfaces:
- Route scope.
GET /session/:id/tasks/:taskId/outputgoes throughwithOwnerReadSession; the WS case usesrequireOwned(read path, matching siblingsession/tasks) and is registered inWS_READ_METHODS. No primary-runtime or cross-session fallback. - File access. Output is resolved by
taskIdinside the owning session's ownbackgroundShellRegistry/monitorRegistry— no client-supplied path reaches the filesystem. The read reusesreadTaskOutputTailwith itsO_NOFOLLOW+fstatidentity guard, control/bidi sanitization, and the 64 KiB clamp; fs errors map to a genericTask output is unavailable.rather than leaking the path or errno. - Reader refactor. The new
maxBytesparameter defaults toMAX_NOTIFICATION_OUTPUT_TAIL_BYTES, and the length is clamped byMath.min(stat.size, maxBytes, MAX_TASK_OUTPUT_TAIL_BYTES), so the pre-existing notification caller keeps its 8 KiB behavior unchanged. - Monitor writer lifecycle. The write stream is created before spawn and torn down on every exit path — spawn failure (both catch blocks), abort handler, and normal cleanup — with an
errorlistener attached, so a failed or late write degrades to a warning instead of an unhandled crash. - UI.
ProcessTaskOutputcalls all hooks before itsif (!supported) return nullcapability gate, so hook order stays stable across daemons with and withoutsession_task_output; the remountkeyand effect deps prevent stale cross-task output.
Remaining review-round items are all Suggestions (untested in-band error path, uncapped monitor output growth, read-permission roots for the advertised monitor path, first-mount scroll anchoring, terminal-task retry) and are not merge blockers.
CI on this head is 23 pass with no failures; the remaining pending checks are not attributable to this PR and are not treated as blockers.

 yiliang114
left a comment
yiliang114
left a comment
There was a problem hiding this comment.
Reviewed at acd56a4 across correctness and security.
Most of the surface checks out: the output routes gate on session ownership at both layers (task ids are internally generated, no cross-session path), output rendering is plain React text with no dangerouslySetInnerHTML/anchor synthesis, the read path is capped at 64 KiB, and the web-shell panel state handles task completion/panel-close transitions without stale updates.
One issue worth addressing before merge — the new monitor capture file has no size cap, details inline.
qqqys
left a comment
qqqys
left a comment
There was a problem hiding this comment.
Re-reviewed at head 941d16b; my earlier approval was dismissed by this push, so this covers the new commit plus the unchanged remainder of the diff.
Previously blocking issue — still fixed. The one Critical from the prior round (R1-10: _qwen/session/tasks/output dispatchable but absent from ALL_QWEN_VENDOR_METHODS, so initialize never advertised it) remains resolved. This push does not touch dispatch.ts; the entry is still present at line 286 with the transport assertion from 5e8d3bd.
New commit 941d16b (bound monitor output capture) — no Critical found. It replaces the unbounded createWriteStream sink with an in-memory rolling tail capped at MAX_TASK_OUTPUT_TAIL_BYTES + 1, flushed through atomicWriteFile. Checked the blocking-risk surfaces:
- The new cap constant resolves correctly.
monitor.tsnow importsMAX_TASK_OUTPUT_TAIL_BYTESfromservices/backgroundShellRegistry.js; that module imports onlynode:fs, task types,atomicFileWrite,debugLogger,no-follow-open,promptIdContext,terminalSafe, andxml— nothing fromtools/monitor. No cycle, so the module-level+ 1cannot evaluate against a TDZ binding. This mattered: an undefined constant would have madebytesToKeepNaN and silently re-introduced the unbounded growth the commit exists to fix. - No stuck-in-
runningpath from the deferred settle.onClose/onErrornow passsettleFromExit/registry.failas a close callback instead of calling them inline, so terminal status waits on the final flush. Every scheduling gap is covered:flushOutputCapture's.finally()clearsoutputWritePromiseand re-runsfinishOutputCapture;writeOutputCaptureis invoked only from the child stdiodatahandler (a macrotask), while that.finally()runs in the preceding microtask drain, sooutputDirtycan never be left true with no flush scheduled; and onceoutputCloseRequestedis set,writeOutputCaptureearly-returns so no new dirty state can appear.settleFromExitalso self-guards onregistration.status !== 'running', so the deferral cannot double-settle. - Close is requested on all exit paths — spawn throw, abort handler, early-spawn-error, and
cleanup(including the already-cleaned-up branch, which forwards the callback). Write failures are caught inside the flush loop and logged, so an unreadable target degrades rather than rejecting out ofexecute(). - Truncation signal preserved. The file is created empty up front (
atomicWriteFileSyncwithnoFollow: true), so a monitor with no output yields size 0 and the reader returnsundefined→ "No output yet". Once the cap is crossed the size is exactly 64 KiB + 1, which keepsreadTaskOutputTail'struncated: start > 0true.noFollowon both write paths also refuses a pre-planted symlink at the output path. - Behavior change is documented, not silently divergent.
docs/developers/tools/monitor.mdand the design doc were updated in the same commit: the prior claim that rate-limited lines "remain in the output file" is corrected to the bounded rolling tail, so the docs no longer promise full retention the code does not provide. - The new behavior is pinned by a real assertion, not a smoke test: it emits a cap-crossing stdout/stderr stream and asserts the exact resulting file size, the exact retained bytes, and
{ truncated: true }fromreadTaskOutputTail.
Rest of the production diff is byte-identical to the previously approved revision (route ownership via withOwnerReadSession / requireOwned, task-id-only lookup with no client-supplied path, O_NOFOLLOW + fstat tail reader, 64 KiB clamp, generic error text, monitor writer teardown, and hook order ahead of the !supported capability gate). Remaining review-round items are all Suggestions and are not merge blockers.
CI was freshly triggered by this push: 8 passing, no failures, the rest still pending. Pending checks and review-pr are not treated as blockers.
yiliang114
left a comment
yiliang114
left a comment
There was a problem hiding this comment.
Light review pass on head 941d16b. No blocking findings. The new GET /session/:id/tasks/:taskId/output endpoint is owner-gated, and the output path is resolved from the session-scoped shell/monitor registry by taskId rather than client input, so there is no arbitrary-path read; readTaskOutputTail keeps the O_NOFOLLOW + identity check and is hard-capped at 64 KiB, failing closed to an 'unavailable' state. Monitor capture is a bounded tail (64 KiB + 1 byte to preserve the truncated signal) written via atomic noFollow writes with settle deferred until the capture closes, and the web-shell side is capability-gated, renders output as text in a
(no injection surface), and copies the exact displayed value. All checks are green at review time (only the automatic review-pr job still running).
…utput

# Conflicts:
#	docs/developers/daemon/00-index.md

|
🤖 Addressed the latest review feedback (round 14/100). What changed, and what I pushed back on: · 已处理最新评审反馈(第 14/100 轮)。改动内容与我反驳保留之处如下: Autofix round summary — PR #10906Feedback disposition[rc:3970931518] R13-1 [Critical] — escape-sequence payload leaks through the capture grammar — AddressedAll five entrances reproduced on the pre-round head with focused failing tests, then fixed at the grammar level in
[rc:3970931527] R14-1 [Critical] — CR frame selector treats a whitespace-only erase pad as the frame — Addressed
Deferred / declinedNone this round. The review body's deferred non-Critical list is explicitly "recorded, not requested in this round" under the convergence posture, and the Conflict notes
VerificationReproduction first (pre-fix, at head
Post-fix checks actually run:
中文说明Autofix 本轮总结 — PR #10906反馈处置[rc:3970931518] R13-1 [Critical] — 转义序列 payload 透过捕获文法泄漏 —— 已处理五个入口全部先在修复前的 head 上用聚焦的失败测试复现,然后在
[rc:3970931527] R14-1 [Critical] —— 回车帧选择器把纯空白擦除填充当成所绘帧 —— 已处理
延后 / 拒绝本轮无。评审正文中的延后非 Critical 列表在收敛姿态下明确为"已记录,本轮不要求修改",而 冲突说明
验证先复现(修复前,head
修复后实际运行的检查:
Deferred non-Critical feedbackCritical-only mode is active: 5 change-producing rounds are complete. The workflow excluded the non-Critical feedback below from this round's actionable sections; the items remain open for human follow-up. Maintainer feedback is deferred only after its author has used 2 regular feedback batches in this window's Critical-only tail; authors at that budget, if any, are named below. (
中文说明已进入仅处理 Critical 的模式:已完成 5 个产生改动的轮次。本轮可执行区域已排除下方非 Critical 反馈;这些条目保持开放,留待人工跟进。维护者反馈仅在其本人于本窗口 Critical-only 阶段已使用 2 批常规反馈预算后才会延后;达到预算的作者(如有)在下方点名。(评论 Base-conflict check · 基分支冲突检查: no conflict with main. · 与 main 无冲突。 🧵 Resolved all 2 selected review thread(s). · 已关闭全部选中的 2 条评审线程。 Re-review when you have a moment. After round 100 this bot stops and leaves the PR for a human. · 有空请复审;第 100 轮后本 bot 停止并将 PR 交给人工。 🧠 Handled by Qwen Code · model/模型 |

Round-4 local verification on a real stack (maintainer) — head
|

| # | Item | Result at 4661b40aa4 |
|---|---|---|
| 1 | Shell output while running and after completion | 91 lines retained after exitCode 0 — stdout line 01…45, stderr line 01…45, SHELL-DONE-MARKER |
| 2 | Monitor with notification throttling | Events 6, Dropped 115, and all 121 captured lines present |
| 3 | Follow at bottom / preserve after scrolling up | Pinned: scrollTop 1246 -> 3082 with scrollHeight - scrollTop = clientHeight = 358 on both samples, content line 044 -> 095. Scrolled to top: scrollTop 0 -> 0 while scrollHeight 3440 -> 4304, content 095 -> 119 |
| 4 | Copy button | Icon lucide-copy -> lucide-check -> lucide-copy; clipboard pasted with a real Cmd+V = 62 chars, byte-identical to the visible <pre> |
| 5 | Daemon without the capability | Same bundle index-CHsT9Vdj.js against a daemon with session_task_output removed (141 -> 140 features): metadata-only, 0 copy buttons, no Output section |
Route validation and the safety guards, re-measured on this head:
kind missing / kind=bogus         -> 400 VALIDATION_FAILED
no Authorization header           -> 401
unknown taskId                    -> 200 in-band {error:"Task output is unavailable."}
symlink planted over the path     -> refused, the target's secret never served
FIFO planted over the path        -> HTTP 200 in 10 ms, daemon not wedged
2. What the two grammar commits genuinely fix — four leaks, measured live on the Monitor path
One probe writes ESC and its final byte in separate write() calls 250 ms apart (an ordinary pipe-chunk split), run once as a background Shell and once as a Monitor.

On the Monitor path these four all went from leaking to clean, and the capture file now carries 0 ESC bytes:
| case | served at this head |
|---|---|
| DCS terminated by ST, payload straddling a chunk | J-dcs KEPT END |
| DCS terminated by BEL | K-dcs-bel KEPT END |
| unterminated DCS leader then a newline | L-dcs-unterm , next line kept |
ST split across chunks (ESC in one chunk, the backslash in the next) |
O-st KEPT END |
The mechanism the commit names is real — strip-ansi matches only the two ESC P bytes and leaves the payload:
stripAnsi("a <ESC> P 1$r0m <ESC> \ KEPT")   ->   "a1$r0m\KEPT"
stripAnsi("a <ESC> P 1$r0m <BEL> KEPT")     ->   "a1$r0mKEPT"
But shell.ts:3871 is untouched by this PR — still outputStream.write(stripAnsi(event.chunk)) with no hold-back — and the same route serves kind=shell. So all four leaks are still live there, visible in the browser:
J-dcs 1$r0m\KEPT END K-dcs-bel 1$r0mKEPT END L-dcs-unterm 1$rpayload O-st 1$r0m\KEPT END
The commit message's "the capture now strips through the same TAIL_* grammar the reader serves with" holds for Monitor only. Closing the Shell half is the natural follow-up — either share the Monitor writer, or leave it, but the design doc should not claim both halves are covered.
3. F1 is not fixed, and it is now written to disk
TAIL_FE_ESC_REGEX is still /\x1b[\x20-\x2f]+(?:[\x30-\x7e]|$)/g. At round 3 that leaked the final byte of split two-byte Fe escapes on the reader side only. Now the Monitor writer uses the same function, so the wrong byte is persisted:
round-3 head   monitor capture file   b'G-split-fe decsc decrc crix END'     (correct)
THIS head      monitor capture file   b'G-fe 7decsc 8decrc ccrix END'        (0 ESC bytes - the 7/8/c are real text on disk now)
Same one-character half-revert as round 3, and at this head it is strictly better in three distinct cases, not one. Pure-function comparison on the real dist:
| input | head | arm C (+ to *) |
|
|---|---|---|---|
teardown chunk tail ESC [ plus a lone 0xe6 |
'tail [<U+FFFD>' |
'tail <U+FFFD>' |
arm C — head leaks the CSI introducer |
split two-byte Fe ESC 7 |
'a7b' |
'ab' |
arm C |
ST as its own fragment ESC \ |
'x\\y' |
'xy' |
arm C — head leaks the ST backslash |
stray ESC W |
'aW313 b' |
'a313 b' |
ambiguous (ESC W is a valid Fe = EPA) |
Over 4 000 modelled Shell capture files (identical bytes on both arms): real characters lost 8 254 on both; garbage characters leaked 10 644 head vs 9 406 arm C; of 1 078 disagreements, arm C correct 108, head correct 0.
Arm C costs exactly two assertions, and both pin a leak rather than a behaviour:
readTaskOutputTail > deletes only the ESC of a residual lone ESC, keeping the byte after it— the ambiguousESC Wcase.MonitorTool > flushes held escape and decoder tails into the capture at close— this one pins'tail [<U+FFFD>', i.e. it asserts that the CSI introducer is persisted. Its own comment says "the readable bytes that followed it stay", but[is the sequence's introducer, not a byte the program wrote.
-const TAIL_FE_ESC_REGEX = /\x1b[\x20-\x2f]+(?:[\x30-\x7e]|$)/g;
+const TAIL_FE_ESC_REGEX = /\x1b[\x20-\x2f]*(?:[\x30-\x7e]|$)/g;
4. F2 (new, Suggestion) — the leaderless-residue rule can serve nothing at all
readTaskOutputTail now peeks one byte before the 64 KiB window; if it is ESC, everything up to the first line break is dropped as residue. With files laid out so the byte before the window is exactly the one named:

| tail shape | boundary byte | served |
|---|---|---|
| has newlines | ESC |
65 493 chars — the real first line RED-TEXT real words… is dropped |
| has newlines | ordinary | 65 531 chars — first line intact |
| no newline at all | ESC |
0 chars — readTaskOutputTail returns undefined, so a 71 537-byte capture renders as No output yet |
| no newline at all | ordinary | 65 531 chars, normal |
Reachable for any single-record stream over 64 KiB — a JSON log line, a base64 blob, minified bundle output — whose window boundary happens to land on an ESC. Bounded probability, total consequence, and the empty result is indistinguishable from a task that genuinely produced nothing. Dropping one line when a break exists is defensible; the firstBreak === -1 branch should fall back to serving the window rather than discarding it.
5. The new truncated semantics fire on ordinary progress bars
Folding droppedFrames into truncated is honest — the CR collapse really does destroy records — and the notice text was softened to match. Worth knowing what it costs in practice: a 104-byte progress bar now carries the truncation notice even though its entire output is on screen.

capture file (104 bytes)   downloading pkg-a <CR> downloading pkg-a 35% <CR> downloading pkg-a 100% done <LF> installed 3 packages <LF> PROGRESS-DONE
served                     truncated = true, 3 lines, all of them shown
pane                       "Showing the latest output"
Not a defect — just a call worth making deliberately, since npm, pip, curl -# and most build tools will now show it.
6. Mutation matrix on the new commits — 12 mutants, 11 killed
The bot's own test-efficacy probe still reports no measurement for this PR, so this is measured rather than assumed. Both new test files are much stronger than at round 3 (which was 4 killed of 8).
| Mutation | Verdict | |
|---|---|---|
| M1 | FE + to * (arm C) |
KILLED (2 tests) |
| M2 | string rule loses its BEL terminator | KILLED |
| M3 | string rule loses its newline lookahead | KILLED |
| M4 | CSI rule loses its end-of-input arm | KILLED |
| M6 | leaderless-residue window rule disabled | KILLED |
| M7 | CR erase-pad rule: trim() dropped |
KILLED |
| M8 | droppedFrames no longer folded into truncated |
KILLED (4 tests) |
| M9 | monitor writer reverts to stripAnsi |
KILLED (4 tests) |
| M10 | monitor hold-back reverts to the round-3 grammar | KILLED (3 tests) |
| M11 | over-cap string payload kept, not discarded | KILLED (2 tests) |
| M12 | findStringPayloadEnd loses its BEL arm |
KILLED (2 tests) |
| M5 | Fe rule loses its end-of-input arm | SURVIVED |
M5 is a coverage gap, not an equivalent mutant: I rebuilt it and a teardown chunk ending in ESC ( serves 'a' at head and 'a(' under the mutant.
7. Suites at this head (macOS — the lane CI skips outside merge_group)
| Suite | Result |
|---|---|
npm run typecheck / npm run lint |
pass / pass |
packages/core PR-touched (backgroundShellRegistry, monitor) |
176 passed |
packages/web-shell PR-touched (4 files) |
1 125 passed |
packages/sdk-typescript daemon (3 files) |
616 passed |
packages/acp-bridge full (37 files) |
1 994 passed / 2 failed |
packages/cli PR-touched (7 files) |
2 570 passed / 2 failed |
Both failures are load-dependent flakes in areas this PR does not touch, and both are green when their file runs alone (bridge.test.ts 920 passed twice; server.test.ts 1 259 passed): preheat > clamps explicit keep-alive to the setTimeout maximum / arms idle timer on preheated channel, and GET /workspace/:id/sessions > reports organized session truncation. They appeared only while the batch ran alongside the daemon and a browser. Round 3 saw the same class in server.test.ts and reproduced it on the merge base.
CI at this head: Qwen Code CI success — Test (ubuntu-latest, Node 22.x), Lint & Static, web-shell E2E Smoke, Integration Tests (no-AK) and both Desktop Shell lanes green; Test (macos-latest) and Test (windows-latest) skipped, which is the gap these local macOS runs fill.
Verdict
The direction of these two commits is right and the Monitor half is materially better than it was at round 3 — four real payload leaks closed, pinned by tests a same-tree revert kills. Before merge I would like the one-character F1 half-revert in section 3, because that defect is now persisted to disk rather than applied at read time, and its two pinning assertions both encode a leak. F2 and the Shell-side writer asymmetry are fine as follow-ups. Nothing here serves wrong data or affects the session-owner binding, the 64 KiB ceiling, or the symlink/FIFO guards, all of which I re-measured and they hold.
中文说明
第四轮本地真实环境验证(维护者)—— head 4661b40aa4
这是对我此前第一轮(5c41a581a6)、第二轮(14ef3e198e)、第三轮(0d2ee20037)报告的续篇。我在新的 worktree 重建了当前 head,重跑了真实 qwen serve + 真实 Chrome 的验证台,重点验证第三轮以来新增的三个实质提交:c491511461(teardown join)、7c511421d4(写入端与读取端共用一套转义语法)、4661b40aa4(补齐剩余语法缺口)。
结论:评审测试计划仍然 5/5,安全护栏仍然成立,两个转义语法提交对 Monitor 链路是一次实质且可观的改进——我实测到它们关闭了四处不同的泄漏。但有两点需要在合入前做决定:
- 我第三轮的 F1 没有被修复,而且
7c511421d4把它从读取端传播到了写入端。 Monitor 的捕获现在经stripOutputControlChars处理,而该函数里TAIL_FE_ESC_REGEX的+缺陷依旧——于是错误的字节现在被永久写进捕获文件,读取端再怎么修也救不回来。我第三轮提出的一字符「只回退一半」方案能修好它,而且在当前 head 上它在三处不同用例上严格更优。 - F2(新发现):新的「无引导符残留」窗口规则在超过 64 KiB 的单记录流上可能什么都不返回,导致一个有 70 KB 输出的任务在界面上显示为「暂无输出」。
两者都不会返回错误数据,都属于显示层面。这两个提交其余我能测到的部分表现都很好——变异矩阵为 12 杀 11,第三轮是 8 杀 4。
验证台 —— worktree 位于 4661b40aa4,node_modules 与 lockfile 一致,npm run build;daemon 用 node packages/cli/dist/index.js serve --port 8941 --workspace <临时 git 仓库>,隔离 HOME;约 60 行假 OpenAI provider 使真实 run_shell_command/monitor 调用可以执行;系统 Chrome;Web Shell 客户端 bundle 为 index-CHsT9Vdj.js(每次测量都记录)。该 head 上 npm run typecheck、npm run lint 均通过。
0. 范围 —— 本 PR 自身贡献中自第三轮以来发生变化的部分
按「本 PR 自身贡献」(每个文件 git diff <merge-base> <head> 的增删行集合,这样两次主干合并不会被计入)对比:
packages/core/src/services/backgroundShellRegistry.ts  + .test.ts   语法改动
packages/core/src/tools/monitor.ts                     + .test.ts   捕获写入器、hold-back、超限丢弃
packages/core/src/services/monitorRegistry.ts                       +8 行:outputCaptureClosed?: Promise<void>
packages/cli/src/ui/AppContainer.test.tsx                           QWEN_HOME 之外再钉住 HOME
packages/web-shell/client/i18n.tsx                                  2 行:「仅显示最近 64 KiB」→「仅显示最新输出」
packages/web-shell/client/components/messages/TasksStatusMessage.test.tsx   1 行:对应断言
本 PR 对其余 39 个文件的贡献与第三轮逐字节一致,那份报告依然覆盖它们。TasksStatusMessage.tsx 本身没有变化,所以下文第 3、4 项只需复核。
1. 评审测试计划 —— 本 head 上 5/5
| # | 项目 | 4661b40aa4 上的结果 |
|---|---|---|
| 1 | Shell 运行中与完成后的输出 | exitCode 0 后仍保留 91 行——stdout line 01…45、stderr line 01…45、SHELL-DONE-MARKER |
| 2 | 触发限流的 Monitor | Events 6、Dropped 115,全部 121 行都在 |
| 3 | 底部跟随 / 上滚后保持 | 跟随:scrollTop 1246 -> 3082,两次采样 scrollHeight - scrollTop = clientHeight = 358,内容 line 044 -> 095。滚到顶部:scrollTop 0 -> 0,scrollHeight 3440 -> 4304,内容 095 -> 119 |
| 4 | 复制按钮 | 图标 lucide-copy -> lucide-check -> lucide-copy;真实 Cmd+V 粘贴得到 62 字符,与可见 <pre> 逐字节一致 |
| 5 | 不声明该能力的 daemon | 同一 bundle index-CHsT9Vdj.js 连到移除 session_task_output 的 daemon(141 -> 140 个 feature):仅元数据,0 个复制按钮,无 Output 区块 |
路由校验与安全护栏,在本 head 上重新实测:
缺少 kind / kind=bogus            -> 400 VALIDATION_FAILED
无 Authorization 头               -> 401
未知 taskId                       -> 200 带内 {error:"Task output is unavailable."}
在输出路径放置符号链接            -> 拒绝,目标文件的秘密内容从未被返回
在输出路径放置命名管道            -> HTTP 200,耗时 10 ms,daemon 未被楔死
2. 两个语法提交真正修好的部分 —— Monitor 链路上四处泄漏,均为实测
一个探针把 ESC 与其终止字节分两次 write() 写出,间隔 250 ms(普通的管道分块),分别以后台 Shell 和 Monitor 各跑一次。
在 Monitor 链路上,下列四项从泄漏变为干净,且捕获文件中 ESC 字节数为 0:
| 用例 | 本 head 返回 |
|---|---|
| 以 ST 结尾、payload 跨分块的 DCS | J-dcs KEPT END |
| 以 BEL 结尾的 DCS | K-dcs-bel KEPT END |
| 未终止的 DCS 引导符后接换行 | L-dcs-unterm ,下一行保留 |
ST 跨分块(ESC 在前一块,反斜杠在后一块) |
O-st KEPT END |
提交信息所述机理属实——strip-ansi 只匹配 ESC P 两个字节,把 payload 留下:
stripAnsi("a <ESC> P 1$r0m <ESC> \ KEPT")   ->   "a1$r0m\KEPT"
stripAnsi("a <ESC> P 1$r0m <BEL> KEPT")     ->   "a1$r0mKEPT"
但 shell.ts:3871 未被本 PR 触及——仍然是逐分块 outputStream.write(stripAnsi(event.chunk)),没有 hold-back——而同一个路由也服务 kind=shell。所以这四处泄漏在 shell 链路上依然存在,并且在浏览器里可见:
J-dcs 1$r0m\KEPT END K-dcs-bel 1$r0mKEPT END L-dcs-unterm 1$rpayload O-st 1$r0m\KEPT END
提交信息里「捕获现在使用与读取端相同的 TAIL_* 语法」只对 Monitor 成立。补上 shell 那一半是自然的后续——要么共用 Monitor 的写入器,要么保持现状,但设计文档不应声称两半都已覆盖。
3. F1 未修复,而且现在被写进了磁盘
TAIL_FE_ESC_REGEX 仍然是 /\x1b[\x20-\x2f]+(?:[\x30-\x7e]|$)/g。第三轮时它只在读取端泄漏被切分的双字节 Fe 转义的终止字节;现在 Monitor 写入端用的是同一个函数,于是错误字节被持久化:
第三轮 head    monitor 捕获文件   b'G-split-fe decsc decrc crix END'   (正确)
本 head        monitor 捕获文件   b'G-fe 7decsc 8decrc ccrix END'      (ESC 数为 0——7/8/c 已成为磁盘上的真实文本)
与第三轮相同的一字符半回退,而在当前 head 上它在三处不同用例上严格更优,而不只是一处。基于真实产物的纯函数对比:
| 输入 | head | arm C(+ 改 *) |
|
|---|---|---|---|
收尾分块 tail ESC [ 加上单独的 0xe6 |
'tail [<U+FFFD>' |
'tail <U+FFFD>' |
arm C——head 泄漏了 CSI 引导符 |
被切分的双字节 Fe ESC 7 |
'a7b' |
'ab' |
arm C |
作为独立片段出现的 ST ESC \ |
'x\\y' |
'xy' |
arm C——head 泄漏了 ST 的反斜杠 |
游离 ESC W |
'aW313 b' |
'a313 b' |
有歧义(ESC W 是合法的 Fe = EPA) |
在 4 000 个模拟 shell 捕获文件上(两臂字节完全相同):丢失的真实字符两臂均为 8 254;泄漏的垃圾字符 head 10 644,arm C 9 406;1 078 处分歧中,arm C 正确 108 次,head 正确 0 次。
arm C 恰好只让两条断言变红,而这两条钉住的都是泄漏本身,而非行为:
readTaskOutputTail > deletes only the ESC of a residual lone ESC, keeping the byte after it——即有歧义的ESC W用例。MonitorTool > flushes held escape and decoder tails into the capture at close——它钉住的是'tail [<U+FFFD>',也就是断言 CSI 引导符会被持久化。该用例自己的注释写着「其后可读的字节保留」,但[是序列的引导符,不是程序写出的可读字节。
4. F2(新发现,建议级)—— 无引导符残留规则可能什么都不返回
readTaskOutputTail 现在会窥探 64 KiB 窗口之前的一个字节;若为 ESC,则把直到第一个换行为止的内容全部当作残留丢弃。构造文件使窗口前一字节恰好是指定字节:
| 尾部形态 | 边界字节 | 返回 |
|---|---|---|
| 含换行 | ESC |
65 493 字符——真实的首行 RED-TEXT real words… 被丢弃 |
| 含换行 | 普通字节 | 65 531 字符——首行完整 |
| 完全没有换行 | ESC |
0 字符——readTaskOutputTail 返回 undefined,于是 71 537 字节的捕获文件在界面上显示为「暂无输出」 |
| 完全没有换行 | 普通字节 | 65 531 字符,正常 |
任何超过 64 KiB 的单记录流都可能触发——一行 JSON 日志、一段 base64、压缩后的打包产物——只要窗口边界恰好落在 ESC 上。概率有界,但后果是全丢,而且这个空结果与「任务确实没有输出」无法区分。存在换行时丢掉一行是可以接受的;firstBreak === -1 这一分支应当回退为照常返回该窗口,而不是整体丢弃。
5. 新的 truncated 语义会在普通进度条上触发
把 droppedFrames 折进 truncated 是诚实的——CR 折叠确实会销毁记录——提示文案也相应做了弱化。值得知道它在实践中的代价:一个 104 字节的进度条现在也会带上截断提示,尽管它的全部输出都在屏幕上。
捕获文件(104 字节)   downloading pkg-a <CR> downloading pkg-a 35% <CR> downloading pkg-a 100% done <LF> installed 3 packages <LF> PROGRESS-DONE
返回                   truncated = true,3 行,全部显示
面板                   「仅显示最新输出」
这不是缺陷,只是一个值得有意识做出的取舍,因为 npm、pip、curl -# 以及大多数构建工具从此都会显示它。
6. 新提交的变异矩阵 —— 12 个变异体,杀死 11 个
机器人自己的 test-efficacy 探针对本 PR 仍无测量结果,所以这部分是实测而非推断。两个新测试文件都比第三轮(8 杀 4)强得多。
| 变异 | 判定 | |
|---|---|---|
| M1 | FE + 改 *(arm C) |
KILLED(2 条用例) |
| M2 | string 规则丢掉 BEL 终止符 | KILLED |
| M3 | string 规则丢掉换行前瞻 | KILLED |
| M4 | CSI 规则丢掉输入结束分支 | KILLED |
| M6 | 停用无引导符残留窗口规则 | KILLED |
| M7 | CR 擦除填充规则去掉 trim() |
KILLED |
| M8 | droppedFrames 不再折进 truncated |
KILLED(4 条) |
| M9 | monitor 写入器退回 stripAnsi |
KILLED(4 条) |
| M10 | monitor hold-back 退回第三轮语法 | KILLED(3 条) |
| M11 | 超限 string payload 保留而非丢弃 | KILLED(2 条) |
| M12 | findStringPayloadEnd 丢掉 BEL 分支 |
KILLED(2 条) |
| M5 | Fe 规则丢掉输入结束分支 | SURVIVED |
M5 是覆盖缺口而非等价变异体:我重新构建后实测,以 ESC ( 结尾的收尾分块在 head 上返回 'a',在变异体上返回 'a('。
7. 本 head 上的本地套件(macOS —— 正是 CI 在 merge_group 之外会跳过的车道)
| 套件 | 结果 |
|---|---|
npm run typecheck / npm run lint |
通过 / 通过 |
packages/core 本 PR 触及(backgroundShellRegistry、monitor) |
176 通过 |
packages/web-shell 本 PR 触及(4 个文件) |
1 125 通过 |
packages/sdk-typescript daemon(3 个文件) |
616 通过 |
packages/acp-bridge 全量(37 个文件) |
1 994 通过 / 2 失败 |
packages/cli 本 PR 触及(7 个文件) |
2 570 通过 / 2 失败 |
两处失败都是本 PR 未触及区域的负载相关抖动,且各自文件单独运行时全绿(bridge.test.ts 两次均 920 通过;server.test.ts 1 259 通过):preheat > clamps explicit keep-alive to the setTimeout maximum / arms idle timer on preheated channel,以及 GET /workspace/:id/sessions > reports organized session truncation。它们只在与 daemon 和浏览器同机批量运行时出现。第三轮在 server.test.ts 上见过同一类抖动,并在 merge base 上复现过。
本 head 的 CI:Qwen Code CI success——Test (ubuntu-latest, Node 22.x)、Lint & Static、web-shell E2E Smoke、Integration Tests (no-AK) 以及两条 Desktop Shell 车道全绿;Test (macos-latest) 与 Test (windows-latest) 被跳过,而这正是本地 macOS 跑批所填补的缺口。
结论
这两个提交的方向是对的,Monitor 那一半相比第三轮有实质提升——关闭了四处真实的 payload 泄漏,并且有同树回退能打红的测试钉住。合入前我希望先落地第 3 节那个一字符的 F1 半回退,因为该缺陷现在是被持久化到磁盘、而不再是读取时才产生,而且钉住它的两条断言编码的都是泄漏本身。F2 与 shell 侧写入器不对称可以作为后续处理。这里没有任何一项会返回错误数据,也不影响会话归属绑定、64 KiB 上限或符号链接/FIFO 护栏——这些我都重新测量过,全部成立。
…re write failures (#10906)
|
🤖 Addressed the latest review feedback (round 15/100). What changed, and what I pushed back on: · 已处理最新评审反馈(第 15/100 轮)。改动内容与我反驳保留之处如下: Autofix round summary — PR #10906Addressed all four actionable Critical findings. Each fix ships with the red-test [rc:3973840767] R13-1 — escape-grammar class (monitor.ts / backgroundShellRegistry.ts)All five measured entrances are closed, sharing the one stripper grammar:
Not done, with reasons:
[rc:3973840774] R15-1 — mid-escape drop destroyed real output (backgroundShellRegistry.ts)Fixed by the same reader rewrite: the drop-to-first-line branch and its [rc:3973840778] R15-2 — over-cap branch sliced away the terminator ESC (monitor.ts)The over-cap branch now keeps a string payload's trailing ESC held [rc:3973840783] R15-4 — silent capture write failures (monitor.ts / monitorRegistry.ts / tasksSnapshot.ts / status types)
Mutation probes
Verification
中文说明Autofix 本轮总结 — PR #10906本轮处理了全部四条可执行的 Critical 发现。每项修复都附带了发现中所点名的 [rc:3973840767] R13-1 —— 转义文法类别(monitor.ts / backgroundShellRegistry.ts)五个实测入口全部关闭,读写两侧共享同一套 stripper 文法:
未做,及原因:
[rc:3973840774] R15-1 —— 转义中途丢弃破坏真实输出(backgroundShellRegistry.ts)由同一处读取端重写修复:丢弃至首个换行的分支及其"清空整个窗口"的支路已 [rc:3973840778] R15-2 —— 超限分支把终止符 ESC 连同载荷一起切掉(monitor.ts)超限分支现在把字符串载荷的尾部 ESC 保留下来( [rc:3973840783] R15-4 —— 捕获写入失败静默(monitor.ts / monitorRegistry.ts / tasksSnapshot.ts / status 类型)
变异探针
验证
Deferred non-Critical feedbackCritical-only mode is active: 5 change-producing rounds are complete. The workflow excluded the non-Critical feedback below from this round's actionable sections; the items remain open for human follow-up. Maintainer feedback is deferred only after its author has used 2 regular feedback batches in this window's Critical-only tail; authors at that budget, if any, are named below. (
中文说明已进入仅处理 Critical 的模式:已完成 5 个产生改动的轮次。本轮可执行区域已排除下方非 Critical 反馈;这些条目保持开放,留待人工跟进。维护者反馈仅在其本人于本窗口 Critical-only 阶段已使用 2 批常规反馈预算后才会延后;达到预算的作者(如有)在下方点名。(评论 Base-conflict check · 基分支冲突检查: no conflict with main. · 与 main 无冲突。 🧵 Resolved all 4 selected review thread(s). · 已关闭全部选中的 4 条评审线程。 Re-review when you have a moment. After round 100 this bot stops and leaves the PR for a human. · 有空请复审;第 100 轮后本 bot 停止并将 PR 交给人工。 🧠 Handled by Qwen Code · model/模型 |
Round-5 local verification on a real stack (maintainer) — head
|

| input | round-4 head | this head |
|---|---|---|
split two-byte Fe ESC 7 / 8 / c / D / M / = / > |
'a7b', 'a8b', … |
'ab' — all seven |
stray ESC W (a valid Fe = EPA, ambiguous) |
'aW313 b' |
'aW313 b' — unchanged, correctly |
unassigned ESC Q / ESC z |
— | 'aQb' / 'azb' — byte kept |
Live on the daemon, same probe as round 4 (a child writing ESC and its final byte in separate write() calls 250 ms apart):
SHELL   served   "G-fe decsc decrc crix END"      (round 4: "G-fe 7decsc 8decrc ccrix END")
MONITOR served   "G-fe decsc decrc crix END"      and the capture file holds 0 ESC bytes
The monitor capture file being clean is the part that mattered most — round 4's version had written 7decsc to disk, where no reader-side fix could recover it.
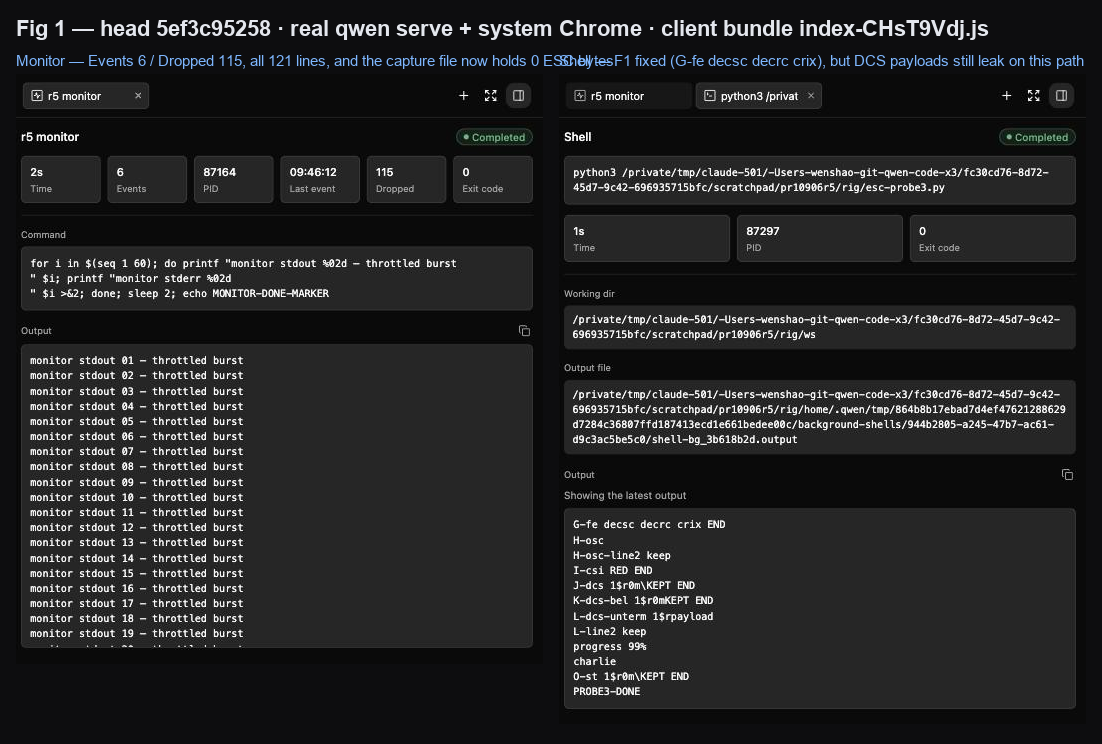
2. F2 is fixed — and better than I asked for
I suggested the firstBreak === -1 branch fall back to serving the window. The commit instead looks back up to 4 096 bytes for the sequence's leader and prepends it so the stripper can remove the whole sequence, which keeps the real first line as well:
tail shape, byte before the window = ESC |
round-4 head | this head |
|---|---|---|
| tail has newlines | real first line dropped (65 493 chars) | 65 532 chars, first line intact, only the [31m residue removed |
| tail has no newline at all | 0 chars — a 71 537-byte capture rendered as No output yet |
65 532 chars served |
3. The new capture-failure surface works end to end
I drove it live: a running monitor, then chmod 500 on its capture directory so every write fails.

served status outputCaptureError = 'atomicWriteFile("…"): EACCES: permission denied…'
model notification <summary>… Output capture failed: atomicWriteFile("…"): EACCES …</summary>
give-up latch the capture froze at 144 bytes / "cap line 12" and stayed there even after
I restored the directory permissions (MAX_OUTPUT_WRITE_FAILURES = 3)
final task status completed, eventCount 25, served output 12 lines
So the tail really is stale — but it is no longer silently stale, which is the whole point of the change. Both the browser and the model are told.
4. F3 (new, Suggestion) — the lookback can serve past the documented 64 KiB ceiling
When the nearest ESC before the window is a stray one on the same line, everything between it and the window is prepended and served, so the response exceeds the cap by that distance:
ESC..window gap      0     100    1000    4000    4095    4096    5000
served chars     65536   65636   66536   69536   69631   65536   65536
over the cap         0     100    1000    4000    4095       0       0
Bounded at MAX_TAIL_SEQUENCE_LOOKBACK_BYTES = 4 096, so the served tail is really "at most 64 KiB + 4 095 bytes". The design doc and the reviewer test plan both say 64 KiB. Either clamp after prepending or state the real bound — this is a one-line call, not a defect.
5. F4 (new, Suggestion) — the capture-failure message is 746 chars and repeats the absolute path
The recorded error embeds the daemon-absolute capture path twice — once in the atomicWriteFile(…) prefix and once in the EACCES body — and it ships to the browser client and into the model-facing <summary>. This PR exists partly because "a daemon-local file path is often not useful to a remote browser"; trimming to the errno plus a basename would fit that better and cost the model far fewer tokens.
6. Still open from round 4 (not a regression, and not introduced here)
shell.ts:3871 is still outputStream.write(stripAnsi(event.chunk)) with no hold-back, and strip-ansi eats ESC P as a two-byte escape — so on kind=shell the DCS payloads still reach the browser, while the Monitor path (which this PR hardened) is clean:
SHELL     J-dcs 1$r0m\KEPT END      K-dcs-bel 1$r0mKEPT END      L-dcs-unterm 1$rpayload
MONITOR   J-dcs KEPT END            K-dcs-bel KEPT END           L-dcs-unterm
Fine as a follow-up; I only ask that the design doc not claim both halves share one grammar.
7. Mutation matrix on the new commit — 12 mutants, 8 killed
| Mutation | Verdict | |
|---|---|---|
| N1 | drop the two-byte rule from the strip chain | KILLED |
| N2 | two-byte rule loses the DEC private pairs [6-9=>] |
KILLED |
| N3 | two-byte rule loses the locking shifts `[cno | }~]` |
| N4 | CSI rule loses its new newline lookahead | KILLED |
| N6 | sequence lookback disabled | KILLED (4 tests) |
| N8 | leading-newline trim after a reconstituted sequence removed | KILLED |
| N10 | writer never gives up after repeated failures | KILLED |
| N11 | first capture-write failure is not recorded | KILLED |
| N5 | Fe rule loses its new newline lookahead | SURVIVED — "a ESC ( LF b" → head 'a\nb', mutant 'a(\nb' |
| N7 | lookback no longer stops at a line break | SURVIVED — an ESC on an earlier line: head serves 65 536 chars starting WINDOW-START, mutant serves 65 776 starting EARLIER LINE THAT MUST NOT BE PULLED IN |
| N12 | discard grammar loses its CSI branch | SURVIVED — a 6 000-byte over-cap CSI through the real monitor: head X-csi REAL-TEXT-AFTER END, mutant X-csi m REAL-TEXT-AFTER END |
| N9 | shrunk-file guard removed | SURVIVED — defensive branch, I did not construct a witness |
The three witnessed survivors are coverage gaps, not equivalent mutants. N7 is the one worth a line of test — it is exactly what keeps F3 bounded to a single line instead of running back across the whole 4 KiB lookback.
8. Reviewer Test Plan and guards at this head
| item | result |
|---|---|
| 1 — Shell after completion | 91 lines, 45 stdout + 45 stderr + SHELL-DONE-MARKER, truncated: false |
| 2 — Monitor with throttling | Events 6, Dropped 115, all 121 captured lines present |
| 4 — Copy button | present and enabled on the detail (1 copy button) |
| 5 — Capability gate | unchanged since round 4 (client contribution byte-identical) |
kind missing / kind=bogus   -> 400 VALIDATION_FAILED
no Authorization header     -> 401
symlink over the path       -> in-band error, the target's secret never served
FIFO over the path          -> HTTP 200 in 12 ms, daemon not wedged
Suites at this head, all green, no flakes this run:
| Suite | Result |
|---|---|
npm run typecheck / npm run lint |
pass / pass |
packages/core (backgroundShellRegistry, monitor, monitorRegistry) |
246 passed |
packages/web-shell PR-touched (3 files) |
1 061 passed |
packages/sdk-typescript daemon (3 files) |
616 passed |
packages/cli (tasksSnapshot, server, acpAgent) |
1 961 passed |
packages/acp-bridge (status, bridge) |
938 passed |
Verdict
My round-4 blocking ask is resolved and I have no blocking item at this head. F1 was fixed with a better mechanism than I proposed, F2 was fixed more thoroughly than I asked, and the capture-failure surface does what it says on a real daemon. F3, F4, the N5/N7/N12 coverage gaps and the Shell-side writer asymmetry are all follow-up sized. From my side this is ready to merge.
中文说明
第五轮本地真实环境验证(维护者)—— head 5ef3c95258
这是对第三轮(0d2ee20037)与第四轮(4661b40aa4)的续篇。我第四轮报告之后又落地了一个提交 5ef3c95258,它把我提的两点都处理了。
结论:F1 与 F2 都已修复,而且 F1 用的机制比我提议的更好。新增的捕获失败上报链路端到端可用。我第四轮的阻断项已解决,当前 head 上我没有阻断项。 下文有两条新的建议级说明(F3、F4),以及第四轮那条按设计仍未处理的 shell 侧写入器不对称。
验证台 —— worktree 位于 5ef3c95258,node_modules 与 lockfile 一致,npm run build;daemon 用 node packages/cli/dist/index.js serve --port 8951 --workspace <临时 git 仓库>,隔离 HOME;约 60 行假 OpenAI provider 使真实 run_shell_command/monitor 调用可以执行;系统 Chrome;Web Shell 客户端 bundle 为 index-CHsT9Vdj.js。npm run typecheck、npm run lint 均通过。
1. F1 已修复 —— 用枚举白名单,这是更正确的做法
我要求的是把 TAIL_FE_ESC_REGEX 的 + 改成 *。提交做了更好的处理:保留 Fe 规则不动,新增
const TAIL_TWO_BYTE_ESC_REGEX = /\x1b(?:[DEHMNOZ]|[6-9=>]|[cno|}~])/g;
它剥离的是已分配的双字节转义,而不碰真正游离 ESC 之后的那个字节——也就是说,它把我第三轮指出的歧义解决掉了,而不是在两侧之间做交换。基于真实产物实测:
| 输入 | 第四轮 head | 本 head |
|---|---|---|
被切分的双字节 Fe ESC 7 / 8 / c / D / M / = / > |
'a7b'、'a8b' …… |
'ab' —— 七个全部 |
游离 ESC W(合法 Fe = EPA,有歧义) |
'aW313 b' |
'aW313 b' —— 保持不变,正确 |
未分配的 ESC Q / ESC z |
— | 'aQb' / 'azb' —— 字节保留 |
在真实 daemon 上跑与第四轮相同的探针(子进程把 ESC 与终止字节分两次 write(),间隔 250 ms):
SHELL   返回   "G-fe decsc decrc crix END"      (第四轮:"G-fe 7decsc 8decrc ccrix END")
MONITOR 返回   "G-fe decsc decrc crix END"      且捕获文件中 ESC 字节数为 0
monitor 捕获文件变干净是最要紧的一点——第四轮那一版已经把 7decsc 写进了磁盘,读取端再怎么修也救不回来。
2. F2 已修复 —— 而且比我要求的更彻底
我建议 firstBreak === -1 那个分支回退为照常返回窗口。提交改为向前回看最多 4 096 字节找到序列引导符并前置拼接,让剥离器可以整段移除该序列,因此真实的首行也保住了:
尾部形态,窗口前一字节 = ESC |
第四轮 head | 本 head |
|---|---|---|
| 尾部含换行 | 真实首行被丢弃(65 493 字符) | 65 532 字符,首行完整,只移除了 [31m 残留 |
| 尾部完全没有换行 | 0 字符——71 537 字节的捕获文件显示为「暂无输出」 | 返回 65 532 字符 |
3. 新增的捕获失败上报链路端到端可用
我实测驱动了它:一个运行中的 monitor,然后对其捕获目录 chmod 500 使每次写入都失败。
返回状态 outputCaptureError = 'atomicWriteFile("…"): EACCES: permission denied…'
模型通知 <summary>… Output capture failed: atomicWriteFile("…"): EACCES …</summary>
放弃闩锁 捕获文件冻结在 144 字节 /「cap line 12」,即使我恢复目录权限后也不再前进
(MAX_OUTPUT_WRITE_FAILURES = 3)
最终任务 status completed、eventCount 25、返回输出 12 行
也就是说尾部确实是陈旧的——但不再是静默陈旧,而这正是本次改动的意义所在。浏览器和模型都被告知了。
4. F3(新发现,建议级)—— 回看拼接可能返回超出文档所述 64 KiB 上限的内容
当窗口之前最近的 ESC 是同一行上的游离 ESC 时,它与窗口之间的所有内容都会被前置拼接并返回,于是响应按该距离超出上限:
ESC 到窗口的间距      0     100    1000    4000    4095    4096    5000
返回字符数        65536   65636   66536   69536   69631   65536   65536
超出上限              0     100    1000    4000    4095       0       0
上界为 MAX_TAIL_SEQUENCE_LOOKBACK_BYTES = 4 096,所以返回的尾部实际上是「最多 64 KiB + 4 095 字节」。设计文档与评审测试计划写的都是 64 KiB。要么在拼接后再裁剪,要么把真实上界写清楚——这是一行的取舍,不是缺陷。
5. F4(新发现,建议级)—— 捕获失败消息长 746 字符且重复了绝对路径
记录的错误把 daemon 的绝对捕获路径嵌入了两次——一次在 atomicWriteFile(…) 前缀里,一次在 EACCES 正文里——并且会送到浏览器客户端和面向模型的 <summary>。本 PR 的立意之一就是「daemon 本地文件路径对远程浏览器通常没有用」;裁剪成 errno 加上文件基名会更契合,也能为模型省下大量 token。
6. 第四轮遗留、非回归、也不是本次引入
shell.ts:3871 仍然是 outputStream.write(stripAnsi(event.chunk)) 且没有 hold-back,而 strip-ansi 会把 ESC P 当作双字节转义吃掉——所以在 kind=shell 上 DCS payload 仍会送到浏览器,而本 PR 加固过的 monitor 链路是干净的:
SHELL     J-dcs 1$r0m\KEPT END      K-dcs-bel 1$r0mKEPT END      L-dcs-unterm 1$rpayload
MONITOR   J-dcs KEPT END            K-dcs-bel KEPT END           L-dcs-unterm
作为后续处理没问题;我只希望设计文档不要声称两半共用同一套语法。
7. 新提交的变异矩阵 —— 12 个变异体,杀死 8 个
| 变异 | 判定 | |
|---|---|---|
| N1 | 从剥离链中删掉双字节规则 | KILLED |
| N2 | 双字节规则丢掉 DEC 私有对 [6-9=>] |
KILLED |
| N3 | 双字节规则丢掉锁定移位 `[cno | }~]` |
| N4 | CSI 规则丢掉新增的换行前瞻 | KILLED |
| N6 | 停用序列回看 | KILLED(4 条用例) |
| N8 | 去掉重建序列后的前导换行裁剪 | KILLED |
| N10 | 写入器在反复失败后永不放弃 | KILLED |
| N11 | 不记录首次捕获写入失败 | KILLED |
| N5 | Fe 规则丢掉新增的换行前瞻 | SURVIVED —— "a ESC ( LF b" → head 'a\nb',变异体 'a(\nb' |
| N7 | 回看不再在换行处停止 | SURVIVED —— 上一行存在 ESC 时:head 返回 65 536 字符、起始为 WINDOW-START,变异体返回 65 776 字符、起始为 EARLIER LINE THAT MUST NOT BE PULLED IN |
| N12 | 丢弃语法丢掉 CSI 分支 | SURVIVED —— 6 000 字节的超限 CSI 经真实 monitor:head 得 X-csi REAL-TEXT-AFTER END,变异体得 X-csi m REAL-TEXT-AFTER END |
| N9 | 去掉文件被截短的守卫 | SURVIVED —— 防御性分支,我没有构造出证人 |
三个有证人的存活者都是覆盖缺口而非等价变异体。其中 N7 最值得补一条用例——正是它把 F3 限制在一行之内,而不是让回看跑遍整个 4 KiB。
8. 本 head 上的评审测试计划与护栏
| 项目 | 结果 |
|---|---|
| 1 —— Shell 完成后 | 91 行,45 stdout + 45 stderr + SHELL-DONE-MARKER,truncated: false |
| 2 —— 触发限流的 Monitor | Events 6、Dropped 115,全部 121 行都在 |
| 4 —— 复制按钮 | 详情上存在且可用(1 个复制按钮) |
| 5 —— 能力门 | 自第四轮以来未变(客户端贡献逐字节一致) |
缺少 kind / kind=bogus   -> 400 VALIDATION_FAILED
无 Authorization 头      -> 401
在路径上放置符号链接     -> 带内错误,目标文件的秘密内容从未被返回
在路径上放置命名管道     -> HTTP 200,耗时 12 ms,daemon 未被楔死
本 head 上的套件,全绿,本次无抖动:
| 套件 | 结果 |
|---|---|
npm run typecheck / npm run lint |
通过 / 通过 |
packages/core(backgroundShellRegistry、monitor、monitorRegistry) |
246 通过 |
packages/web-shell 本 PR 触及(3 个文件) |
1 061 通过 |
packages/sdk-typescript daemon(3 个文件) |
616 通过 |
packages/cli(tasksSnapshot、server、acpAgent) |
1 961 通过 |
packages/acp-bridge(status、bridge) |
938 通过 |
结论
我第四轮的阻断项已解决,当前 head 上我没有阻断项。 F1 用了比我提议更好的机制修复,F2 修得比我要求的更彻底,捕获失败上报链路在真实 daemon 上确实做到了它所声称的事。F3、F4、N5/N7/N12 的覆盖缺口以及 shell 侧写入器不对称都是后续量级的事项。从我这边看,可以合入。
|
🤖 AutoFix stopped: this counting window now contains 3 agent time-budget exhaustions (pushed rounds in between included; this round itself may have failed differently). That is 3 full agent runs that pushed nothing. A human should split or reduce the PR (or raise the agent time budget AND its step backstop together), then comment
See the Qwen Autofix agent step logs for model/tool output. 中文说明🤖 AutoFix 已停止:当前计数窗口内已累计 3 次时间预算耗尽(含其间推送过的轮次;本轮本身可能以别的方式失败)。即 3 次完整 agent 运行没有推送任何内容。应由人工拆分或缩减该 PR(或同时提高 agent 时间预算与其步骤兜底),然后评论 Run log: https://github.com/QwenLM/qwen-code/actions/runs/34451132365 🧠 Handled by Qwen Code · model/模型 |
 qwen-code-dev-bot
added
the
autofix/needs-human
|
⏸️ Takeover paused: this PR reached its round cap (100/100). Comment 中文说明⏸️ 托管已暂停:本 PR 达到轮次上限(100/100)。评论 |
|
@qwen-code /resolve |

Both sides grew legacySessionTelemetryRoutes from the same 69-route base,
so the drift-guard counts collided:

- this PR added GET /session/:id/tasks/:taskId/output  -> 70 routes / 68 handler_resolved
- main added GET+POST /session/:id/sources and
  DELETE /session/:id/sources/:sourceId               -> 72 routes / 70 handler_resolved

The route table itself auto-merged with all four entries, so the assertions
take the union: 73 routes, 71 handler_resolved, 2 pre_resolved (unchanged).
|
Qwen Code resolved the merge conflicts and pushed the branch update. Root causeMain's Semantic, not merely adjacentThe route table auto-merged: the four entries sit in disjoint regions and all survived. The counters did not — each side wrote a total that must include the other's routes, so taking either parent under-counts and fails the guard. Resolution is the union, verified by counting the merged table: // telemetry.test.ts
it('contains 73 unique routes with the audited 71/2 attribution split', ...)
expect(keys).toHaveLength(73); expect(new Set(keys).size).toBe(73);
/* handler_resolved */ ).toHaveLength(71); // 67 base + 1 ours + 3 theirs
/* pre_resolved */ ).toHaveLength(2); // untouched by either side
// telemetry-catalog.test.ts
expect(registered).toHaveLength(73); expect(registered).toEqual(catalog);Load-bearing
Not verifiedNo build, typecheck, lint or tests were run. Two non-conflicted dependents, checked statically:
中文说明根因:main 的 语义冲突,非单纯相邻:路由表自动合并成功(四条条目区域不重叠,全保留),冲突在计数——双方的总数都须含对方路由,取任一父提交都会少算并使守卫失败。故取并集,已统计表核实:73 条路由、71 条 关键约束: 未能验证:未跑构建、类型检查、lint 或测试。仅静态核查两个非冲突依赖: |

 doudouOUC
left a comment
doudouOUC
left a comment
There was a problem hiding this comment.
Review — head 508b31b1
Note on which commit this is against. The head moved while I was reviewing (from 5ef3c95 to 508b31b1), and I re-anchored everything below to 508b31b1. If it moves again, treat the line references as needing re-checking rather than as findings.
Reviewed by reading the diff and the affected files at this SHA. No local test run.
Verdict: ESCALATE to maintainer, with no Critical from me. 49 files across packages/core/src/{services,tools,utils}, packages/cli/src/serve/**, packages/acp-bridge, packages/sdk-typescript and packages/web-shell — cross-package, and it adds a new daemon session route plus a capability flag, so it needs maintainer sign-off on the route contract rather than mine. What I could verify myself, I did, and it held up; details below so the next reader does not have to redo it.
The O_NONBLOCK hardening is correct, and the reasoning is the good kind
packages/core/src/utils/no-follow-open.ts, both variants:
-  const baseFlags = fs.constants?.O_RDONLY ?? 0;
+  const baseFlags =
+    (fs.constants?.O_RDONLY ?? 0) | (fs.constants?.O_NONBLOCK ?? 0);
A FIFO planted under the workspace's own .qwen/ would otherwise block open(2) until a writer appears, and the !stat.isFile() guard only runs after the open returns — so the guard cannot save you, and the stall is daemon-wide. O_NONBLOCK is a no-op for regular files and makes the FIFO open return immediately so the existing fstat check fails closed. The flag does persist on the returned fd, but since non-regular files are rejected post-open, no caller can end up reading EAGAIN off a socket or chardev. This is a shared core utility, though, which is part of why I am escalating rather than approving: every existing caller inherits the flag change.
Web Shell conventions — checked, clean
ProcessTaskOutput in packages/web-shell/client/components/messages/TasksStatusMessage.tsx is a plain function component that owns its refs (outputElementRef, outputValueRef, followNextOutputRef) and renders no portal, so the React.forwardRef requirement for ref-sensitive wrappers and the useWebShellPortalRoot() requirement for portalled components do not apply here. No data-web-shell-* attribute or --web-shell-* variable is disturbed.
The polling effect is well-behaved: an active flag guards every then/catch/finally, the interval is cleared in the cleanup, and the parent remounts via key={${currentTask.kind}:${currentTask.id}} so state cannot leak across tasks. I did stop on the deps list including task.runtimeMs, which changes on every tasks poll and therefore tears down and re-creates the interval before it can fire — but the comment there already says exactly that, and states that the interval exists for cross-session restored tabs which never receive a snapshot advance. Intentional and documented; no finding.
Suggestion — loading is never cleared on the unsupported path
Same component: loading initialises to true, the effect returns early on if (!supported) return, and nothing resets it. It is unobservable today because if (!supported) return null; short-circuits the render before any consumer sees it, so this is not a bug — but it is a state field whose invariant is maintained by a return null several lines away. Initialising loading to supported would make the two agree locally and survive someone later rendering a placeholder instead of null.
CI picture at this head
Mostly green, including Lint & Static, Integration Tests (no-AK, No Sandbox) and Real daemon E2E. Still outstanding: Serve A/B (ubuntu-latest) and Test (ubuntu-latest, Node 22.x) are pending, and Test (macos-latest) / Test (windows-latest) report skipping. Given this adds a daemon route and a capability flag, I would want Serve A/B green before merge, and I would not read the skipped platform lanes as cross-platform coverage for the no-follow-open.ts change — O_NONBLOCK and O_NOFOLLOW availability is exactly where platforms differ.

|
@qwen-code /triage |

qqqys
left a comment
qqqys
left a comment
There was a problem hiding this comment.
Critical-only review pass at head 508b31b1ec1c0c145988540a17b2904ebb6f0ff6. Every distinct Critical still open on this PR is verified fixed by reading the current head code, and the independent scan found no new merge-blocking defect. The outstanding automated change request cites the findings below; each is addressed at this head, so those threads can be closed against this evidence.
Open Critical threads, re-verified on this head
- R2-1 - monitor capture decoded each pipe chunk with a raw
toString('utf-8'), baking U+FFFD into the persisted file - fixed.packages/core/src/tools/monitor.tsimportsStringDecoderand gives each stream its own instance (decoder: new StringDecoder('utf8')on both the stdout and stderr buffers, with the comment that a shared one would corrupt the other), decoding throughbuffer.decoder.write(data)so a multi-byte codepoint split across pipe chunks is reassembled. On teardown it flushesbuf.decoder.end()and strips the concatenationheldEscape + decoderResidueas one unit, so a codepoint or sequence straddling the final chunk is not corrupted either. - R2-4 - ANSI sequences straddling two chunks survived per-chunk
stripAnsiand were persisted literally - fixed. The capture now holds back a trailing incomplete escape sequence per buffer (buffer.heldEscape) and prepends it to the next chunk, with the comment that a chunk-final fragment would otherwise persist the reassembled sequence's debris; the terminator-straddling case keeps the ESC held so the next chunk's first byte decides what it starts, and an over-cap leader is dropped from that chunk rather than persisted. On the read sidestripOutputControlCharsremoves whole OSC/DCS/CSI/Fe/two-byte sequences before the per-character backstop, andreadTaskOutputTailreconstitutes a window that opens mid-sequence through a bounded 4 KiB lookback. - R2-2 - the telemetry route drift guard pinned stale counts, failing two existing tests - fixed.
packages/cli/src/serve/server/telemetry.test.ts(+4/-4) andtelemetry-catalog.test.ts(+1/-1) carry the bumped pins at this head, andTest (ubuntu-latest, Node 22.x), which runs that suite, concludes success on this commit. - R2-3 - an unknown or evicted taskId threw
RequestError.invalidParams, surfacing a client miss as a 5xx / -32603 server fault - fixed.buildSessionTaskOutputStatusinpackages/cli/src/acp-integration/acpAgent.tsnow returns{ v, sessionId, taskId, kind, output: '', truncated: false, error: 'Task output is unavailable.' }when the registry has no entry, and the same fail-closed payload whenreadTaskOutputTailreports an error. The remainingRequestError.invalidParamsthrows in the ext-method arm are reserved for genuinely malformed request parameters (missingsessionId/taskId, ataskKindoutsideshell | monitor). - R3-1 - cross-session restored task tabs read output from the active session - fixed.
packages/web-shell/client/App.tsxnow overridesgetTaskOutput: (taskId, kind) => workspace.client.sessionTaskOutput(tab.sourceSessionId, taskId, kind)incrossSessionActionsalongsidegetTasksandcancelTask, so a restored tab reads through its owning session. - R4-1 - the client-triggerable read opened the task-owned file without
O_NONBLOCK, so a planted FIFO could stall the daemon's main thread - fixed.packages/core/src/utils/no-follow-open.tsnow buildsbaseFlagsas(fs.constants?.O_RDONLY ?? 0) | (fs.constants?.O_NONBLOCK ?? 0)in bothopenSyncNoFollowandopenNoFollow, including the fallback branch used whereO_NOFOLLOWis unavailable.readTaskOutputTailopens throughopenSyncNoFollow(outputFile)and only then reachesfs.fstatSync(fd)withif (!stat.isFile() || stat.size <= 0) return undefined;, so the FIFO open returns immediately and the guard fails closed instead of blocking upstream of it.
Current scan
- Route ownership and scoping.
GET /session/:id/tasks/:taskId/outputinpackages/cli/src/serve/routes/session.tsis wrapped inwithOwnerReadSession, validatestaskIdpresence andkindagainstshell | monitorwith a 400VALIDATION_FAILEDbefore any read, setsCache-Control: no-store, and delegates to the resolved runtime's own bridge (runtime.bridge.getSessionTaskOutputStatus(sessionId, taskId, kind)), so there is no primary-runtime fallback and no cross-session lookup path. - Bounded, race-aware tail read.
readTaskOutputTailcaps the window atMath.min(stat.size, maxBytes, MAX_TASK_OUTPUT_TAIL_BYTES)(64 KiB), detects the file shrinking under the read (bytesRead <= lookbackreturns undefined rather than serving a short or wrong window), and reports a lossy carriage-return frame collapse throughdroppedFramesfolded intotruncatedinstead of silently discarding records. - Client surface.
getTaskOutputinpackages/web-shell/client/daemon/session/actions.tsruns throughwithActionTimeout, the action type is declared onDaemonSessionActions, the capability gate keeps older daemons on the metadata-only view, and the four new UI strings exist in both EN and ZH.
CI
Every non-skipped check on this head concluded success, including Test (ubuntu-latest, Node 22.x), Lint & Static, Serve A/B, web-shell E2E Smoke, Capture web-shell visuals, both Desktop Shell lanes, Integration Tests (no-AK), Live Host and the real-daemon E2E lanes. Nothing is failing, cancelled or still running.
Still open, non-blocking
The remaining unresolved threads are Suggestion-level and were not treated as gates: test pinning for the hard-cap operand, the copy button's unavailable and clipboard-failure paths, the capability-fallback render gate, the unavailable-to-recovered transition, the truncation notice's negative case, WS_READ_METHODS read classification, and the unpinned lockedIn-style label widths.
|
🔓 Takeover auto-released: the autofix loop paused on this PR 3 day(s) ago (🤖 AutoFix stopped: this counting window now contains 3 agent time-budget exhaustions (pushed rounds in between included;) and no re-arm followed, so the 中文说明🔓 已自动释放接管:autofix 循环在 3 天前暂停于此 PR(🤖 AutoFix stopped: this counting window now contains 3 agent time-budget exhaustions (pushed rounds in between included;),此后无人重新武装,现移除 |
qwen-code-dev-bot
removed
the
autofix/takeover
qqqys
left a comment
qqqys
left a comment
There was a problem hiding this comment.
This review corrects our own prior approval at this head and flips our verdict. It files no new finding: the four [Critical] threads named below were filed by the automated reviewer on 2026-09-10 and are still open. Nothing here re-argues them, and no equivalent feedback is being duplicated.
State as read immediately before posting this review: head 508b31b1ec1c0c145988540a17b2904ebb6f0ff6 (unmoved since 2026-09-10), reviewDecision=CHANGES_REQUESTED, mergeable_state=dirty.
1. What is void in our APPROVED review of 2026-09-11T23:00:58Z (id 5184081272)
Two claims, both falsified at the same head they were made about:
- "Every distinct Critical still open on this PR is verified fixed by reading the current head code, and the independent scan found no new merge-blocking defect."
- "Still open, non-blocking — The remaining unresolved threads are Suggestion-level and were not treated as gates."
A complete review-thread census at this head (cursor-paginated, totalCount=111 fetched=111 MATCH=True) reads 87 unresolved threads, 21 of which open with a [Critical] comment. Four are anchored at this head with isResolved=false, isOutdated=false:
| thread | location |
|---|---|
| R13-1 | packages/core/src/services/backgroundShellRegistry.ts:73 |
| R15-3 | packages/acp-bridge/src/status.ts:840 |
| R17-1 | packages/core/src/services/backgroundShellRegistry.ts:172 |
| R17-2 | packages/core/src/services/backgroundShellRegistry.ts:84 |
That approval enumerated six findings from earlier rounds (R2-1, R2-4, R2-2, R2-3, R3-1, R4-1) and never mentioned these four. Its "remaining unresolved threads are Suggestion-level" sentence is therefore wrong as written: it covers 21 unresolved [Critical] threads, not only Suggestions.
2. What we independently re-measured this round: R17-1 is real, and it is a regression
We are not taking the automated finding on faith — we executed it against a checkout of this head.
Location. readTaskOutputTail in packages/core/src/services/backgroundShellRegistry.ts. The window itself is correctly capped at :166 (length = Math.min(stat.size, maxBytes, MAX_TASK_OUTPUT_TAIL_BYTES)), but :205-211 then scans the lookback prefix (:171, bounded by MAX_TAIL_SEQUENCE_LOOKBACK_BYTES = 4096, :44) for a preceding ESC and prepends buffer.subarray(i, lookback) on top of the window. Between there and the return { text: trimmed } at :228-231 the only reductions are stripOutputControlChars (:217), normalizeOutputCarriageReturns (:217), a conditional single leading \n removal and a trimEnd() (:223-225). There is no re-clamp to maxBytes. When the stripper does not consume the prepended bytes — because that ESC leads a sequence that already closed before the window, or leads no recognised sequence at all — every real byte between it and the window start is served in addition to the full window.
Trigger. Any capture file with an ESC in the ≤4096 bytes before the served window and no line break between them. That is ordinary ANSI-coloured child output, not an adversarial input.
Impact. The served text exceeds the caller's byte budget by up to 4096 bytes. Measured on this head:
| case | file bytes | maxBytes |
served | over cap |
|---|---|---|---|---|
ESC [ W + 19 real bytes + 11-byte window |
33 | 11 | 30 | yes |
zz\n + ESC[31m + b×4091 + a×65536 |
69635 | 65536 | 69627 | yes |
control: same file, no ESC before the window |
69630 | 65536 | 65536 | no |
control: default caller (:674, 8192), no ESC |
9003 | 8192 | 8192 | no |
Both controls stay exactly at their cap, so the overflow is caused by the prepend and not by the harness. The second row breaks the 64 KiB bound (MAX_TASK_OUTPUT_TAIL_BYTES, :38) that the task-output endpoint documents, and the first row's shape reaches the pre-existing shell <output-tail> notification at :674, which calls with the default MAX_NOTIFICATION_OUTPUT_TAIL_BYTES = 8192.
Note one correction to the automated thread: its first witness quotes 31 bytes for an 11-byte request; our execution measures 30. The mechanism and the second witness (69627) agree exactly — we derive that figure from the constants alone before running anything (3+5+4091+65536 = 69635 file bytes ⇒ length = 65536, start = 4099, lookback = 4096, prepend ESC[31m+b×4091 ⇒ strip leaves 4091 + 65536 = 69627) — but where the two differ, 30 is the measured value.
Base arm — this is a regression, not pre-existing surface. At merge base 779cfe913bd1dd8063cc822fecd5128ccacc2769 the function is readOutputTail(outputFile) with no maxBytes parameter: MAX_TAIL_SEQUENCE_LOOKBACK_BYTES does not exist anywhere in the file, and the read is Buffer.allocUnsafe(length) → fs.readSync(fd, buffer, 0, length, start) → buffer.subarray(sliceOffset, bytesRead). A subarray of a length-sized buffer, passed only through a stripper and a trimEnd, cannot exceed length. So the base served text was structurally within budget and this diff introduces the over-cap path.
Why the existing test cannot see it. backgroundShellRegistry.test.ts:741 (it('limits output-tail to the retained byte budget')) builds its fixture at :745 as 'prefix-' + 'a'.repeat(MAX_NOTIFICATION_OUTPUT_TAIL_BYTES) + '\nlast line\n' and asserts not.toContain('prefix-') at :757. There is no ESC before prefix-, so the fixture exercises exactly our third control row — the bounded path — and passes whether or not the prepend is clamped.
Fix direction. Either clamp the served text to maxBytes after stripping (take the trailing maxBytes bytes of trimmed, and keep truncated true when that clamp bites), or bound the prepend itself so prependLength + windowLength <= maxBytes by shrinking length before the read. Then extend the :741 fixture with a second case that places an ESC immediately before prefix-, which is the mutation the current pin cannot detect.
3. What is unaffected
The six fix verifications in that approval — R2-1 (StringDecoder per stream in monitor.ts), R2-4 (held-escape reassembly plus stripOutputControlChars/lookback on the read side), R2-2 (telemetry pin bumps), R2-3 (buildSessionTaskOutputStatus failing closed instead of throwing invalidParams), R3-1 (crossSessionActions.getTaskOutput reading through tab.sourceSessionId), R4-1 (O_NONBLOCK in no-follow-open.ts plus the isFile() guard) — are each cited to a specific file and line on a different code path from the one above. They were not re-measured this round and we do not retract them; the author and maintainers can still rely on them.
4. What must be read with caution
That approval's "Bounded, race-aware tail read" bullet says readTaskOutputTail "caps the window at Math.min(stat.size, maxBytes, MAX_TASK_OUTPUT_TAIL_BYTES) (64 KiB)". Read as a statement about length at :166 it is literally true, and the race detection it describes (bytesRead <= lookback returning undefined) is real. It must not be quoted as bounding the served text, which is what section 2 falsifies.
5. What we did not assess
R13-1 (the hand-rolled ECMA-48 grammar being narrower than a real VT parser), R15-3 (outputCaptureError produced and serialized but rendered by no task-detail surface) and R17-2 (the five-pass .replace() chain not being closed under deletion-adjacency) remain the automated reviewer's findings at this head. We did not independently verify them this round and take no position on their severity. They are listed above only because our approval's universal claim covered them.
6. Gate state and scope of this action
reviewDecision is already CHANGES_REQUESTED and mergeable_state is dirty, so this review changes nothing about mergeability today. Its purpose is to remove a misleading signal: our APPROVED row is currently live at head against 21 unresolved [Critical] threads, and it is the only reasoned approval on the PR. We are superseding our own row only — the maintainer approval submitted at 2026-09-11T22:52:39Z is theirs and we say nothing about it. We are not withdrawing or re-filing any dismissed review, and we are not asking for the four threads to be re-litigated; they are open and, for R17-1, now independently confirmed.
|
@qwen-code /resolve |
|
Qwen Code attempted to resolve merge conflicts but the run did not complete successfully. Check the workflow run for full logs. |

Review follow-up and verification reportCommit: The follow-up fixes the confirmed control-filter grammar/adjacency issues, strict returned-byte bound, capture-failure visibility and recovery, and a terminal Monitor capture-flush race. The full build, typecheck, bundle, lint, targeted Core/CLI/ACP/SDK/Web Shell tests and 41 daemon-route integration tests passed locally. Two clean self-audit passes and independent review found no remaining confirmed Critical. Remote CI is running separately. E2E and regression verificationVerified the rebuilt CLI with a real Monitor child process and a localhost mock model. Split escapes, embedded controls, oversized OSC payloads terminated by C1 ST/CAN, and ordinary Unicode text produced the expected captured output and served tail. All seven output lines survived even when event notifications were throttled. The original parser/reader witnesses now pass: no measured escape residue, no ordinary text lost through adjacent escapes, and exactly 65,536 bytes returned for the former 69,627-byte overflow case. Capture failures show a notice in Web Shell and TUI while retaining captured text; recovery clears the warning. A cancelled monitor's task-output request stays pending until the final capture flush completes, then returns the final bytes. Results: 45 focused regression tests passed, plus the bundled-CLI capture assertion. This combines headless CLI E2E with component and ACP endpoint tests; it does not claim interactive browser E2E or a physical disk-full test. Tested bundle SHA-256: 中文:已合并 main 并处理冲突,修复控制序列清理、输出字节上限、捕获失败提示及取消时末尾输出读取竞态。本地构建、类型检查、打包、lint、相关定向测试及 41 项路由集成测试通过;最终实测和回归验证结果如下述报告。远端 CI 正在运行,未将本地测试结果等同于远端 CI 通过。 |
Review follow-up scopeTracked in #12849. This PR has already passed through more than 17 review rounds. Following AGENTS.md’s review-convergence rule, this update fixes confirmed correctness defects and merge regressions. The following remaining Suggestion families are explicitly deferred rather than represented as fixed. Repeated round-2/3/4 copies are grouped under their original id; each linked thread retains the detailed request.
R1-5 (CI collection) is covered by the current no-AK integration script and the 41-test integration run. R1-12 (unbounded file) is already fixed by the rolling tail; R2-11 (hard-cap coverage) is addressed in this update. 中文:本 PR 已经历超过 17 轮审查,按仓库约定,本轮只修复已确认的正确性问题和合并回归。上表逐项记录仍需后续处理的建议,并保留原评论链接;这些建议不冒充已修复。R1-12 已由滚动尾部解决,R2-11 的硬上限测试已补齐。 |
|
Fixed the Validation: the exact 中文:已补齐遗漏的繁体中文文案,修复严格 i18n 检查失败。原始失败命令、本地构建与类型检查、打包和 161 项相关测试均通过,打包产物也已独立复核。远端 Lint & Static 已完整通过,包含原先失败的 i18n 检查及后续全部静态检查;其他测试与评审尚在运行,当前没有其他失败项。 |
This branch has not been deployed
6 participants


What this PR does
This PR makes captured Shell and Monitor output directly readable in the Web Shell task detail panel. Monitor stdout and stderr are now persisted alongside the existing Shell capture, and the daemon exposes a live-session-owner-scoped endpoint that returns a sanitized tail of at most 64 KiB.
The task detail shows live and terminal output, explicit empty/unavailable/truncated states, and a copy action. Web Shell and TUI show capture failures without hiding output already captured, and clear the warning after capture recovers. A shared streaming filter removes terminal control sequences without deleting adjacent log text. When an overflowing output box is already at the bottom, new output keeps it pinned there; once the user scrolls upward, refreshes preserve that position. Older daemons retain the existing metadata-only view through capability detection.
Why it's needed
Web Shell users could previously see task metadata and an output-file path, but not the output itself. Monitor notifications are not rendered as running output in the main Web Shell conversation, and a daemon-local file path is often not useful to a remote browser. This gives users a direct, bounded, session-scoped way to inspect long-running process output without depending on notification rendering or arbitrary filesystem access.
Reviewer Test Plan
How to verify
Evidence (Before & After)
scrollTop=1156to1192; after manually scrolling up it stayed atscrollTop=0, and the copied 2567-character value exactly matched the visible snapshot.Additional real-session evidence: completed Shell and Monitor tasks retained stdout/stderr lines 01–45; a Monitor with
eventCount=49anddroppedLines=41still displayed all 90 captured output lines.Tested on
Environment (optional)
macOS with the production Web Shell build, an isolated local daemon, system Chrome in headless mode, and real Shell/Monitor tool invocations.
npm run build,npm run typecheck,npm run lint, targeted Core/ACP/CLI/SDK/Web Shell tests, and the focused Web Shell task-detail suite all passed.Risk & Scope
Linked Issues
N/A
中文说明
本 PR 做了什么
本 PR 让 Web Shell 任务详情面板可以直接查看捕获的 Shell 和 Monitor 输出。Monitor 的 stdout 和 stderr 现在会像现有 Shell 输出一样持久化,daemon 新增一个严格绑定到实时会话 owner 的接口,最多返回经过清理的最近 64 KiB 输出。
任务详情会展示运行中和终态输出,并提供空输出、不可用、已截断等明确状态以及复制操作。Web Shell 和 TUI 会显示捕获失败提示,同时保留已捕获输出,并在捕获恢复后清除提示。共享的流式过滤器会移除终端控制序列,同时保留相邻日志文本。当输出框已经溢出且位于底部时,新输出会继续跟随到底部;用户向上滚动后,后续刷新会保持其滚动位置。通过 capability 检测,旧 daemon 继续使用原有的仅元数据界面。
为什么需要
此前 Web Shell 用户只能看到任务元数据和输出文件路径,无法直接看到输出。Monitor 通知不会作为运行中输出呈现在 Web Shell 主对话里,而 daemon 本地文件路径对远程浏览器通常也没有用。该改动提供了一种直接、有大小上限且受会话约束的方式来查看长时间运行的进程输出,不依赖通知渲染,也不会开放任意文件系统读取能力。
评审测试计划
如何验证
证据(改动前后)
scrollTop=1156跟随到1192;手动向上滚动后保持在scrollTop=0;复制出的 2567 个字符与可见快照逐字一致。其他真实会话证据:已完成的 Shell 和 Monitor 均保留 stdout/stderr 第 01–45 行;一个
eventCount=49、droppedLines=41的 Monitor 仍显示了全部 90 行捕获输出。测试系统
环境(可选)
macOS,使用生产 Web Shell 构建、隔离的本地 daemon、系统 Chrome 无头模式以及真实 Shell/Monitor 工具调用。
npm run build、npm run typecheck、npm run lint、Core/ACP/CLI/SDK/Web Shell 定向测试和 Web Shell 任务详情专项测试均通过。风险与范围
关联 Issue
无